1.2 Mirror into the trust boundary
Overview
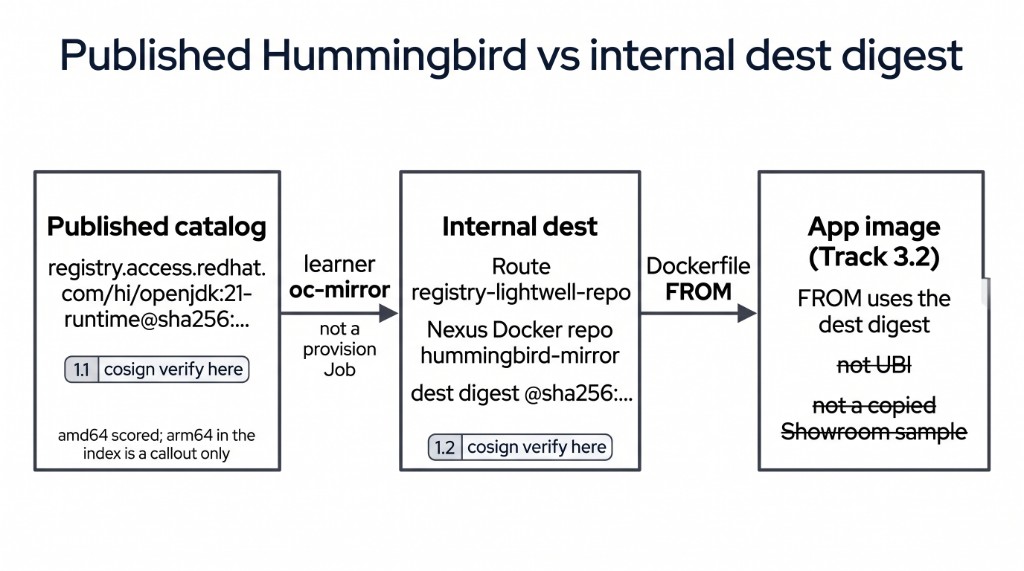
The dest Docker repo hummingbird-mirror starts empty. You finish the incomplete ImageSetConfiguration, start the learner Job from ConfigMap oc-mirror-tooling, and cosign verify the internal digest you record. You already verified the published pin in 1.1. This Check is the digest inside the enterprise.
Why it matters
Builds, GitOps, and admission must pull a dest digest inside the enterprise. They must not pull registry.access.redhat.com at build time. Signatures need to land on dest with the image so you can still verify after the mirror.
What does it solve
-
Catalog images that never entered your registry
-
Signatures stripped on mirror
-
Treating public verify as enough
-
Confusing the Lightwell Maven path with the Docker dest
Why dest is empty
An enterprise DMZ host runs oc-mirror. This Showroom is the in-cluster stand-in, with Nexus hosted Docker hummingbird-mirror as dest. Dest starts empty so you author the ImageSet and run the Job.
|
A Python Hummingbird base uses the same ImageSet pin-and-mirror idea. This Check is the Java |
Discover dest + incomplete ImageSet
oc -n lightwell-repo get configmap demo-userinfo-lightwell-repo \
-o jsonpath='dest={.data.dest_registry_host}{"\n"}repo={.data.dest_registry_repo}{"\n"}docker={.data.dest_registry_docker}{"\n"}pre_mirror={.data.oc_mirror_pre_stage_scored_image}{"\n"}'oc -n lightwell-repo get configmap imageset-configuration \
-o jsonpath='{.data.imageset-config\.yaml}'oc -n lightwell-repo get configmap oc-mirror-tooling \
-o jsonpath='{.data.example-imageset\.yaml}'Worked example (not the Check)
UBI, not Hummingbird. If imageset-configuration still names this image, the Check fails.
# Worked example ONLY — ubi-minimal. The scored ImageSet must be the Hummingbird digest pin.
kind: ImageSetConfiguration
apiVersion: mirror.openshift.io/v2alpha1
mirror:
additionalImages:
- name: registry.access.redhat.com/ubi9/ubi-minimal:latestYour change: ImageSet
oc -n lightwell-repo get configmap demo-userinfo-lightwell-repo \
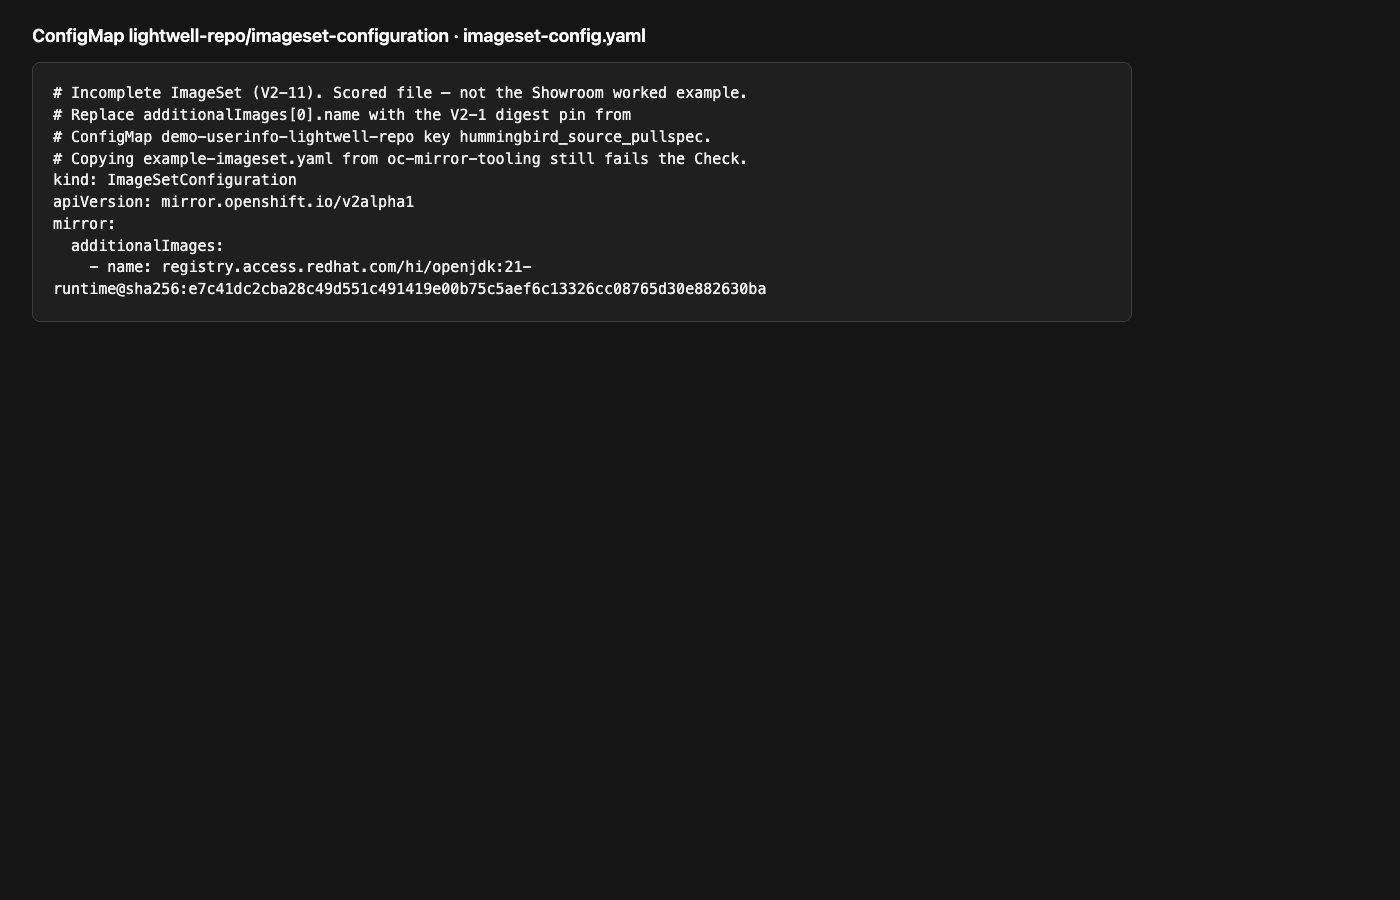
-o jsonpath='{.data.hummingbird_source_pullspec}{"\n"}'Edit ConfigMap imageset-configuration in namespace lightwell-repo so mirror.additionalImages[0].name is that pull spec (digest, not :latest). The seed looks like:
kind: ImageSetConfiguration
apiVersion: mirror.openshift.io/v2alpha1
mirror:
additionalImages:
- name: REPLACE_ME_HUMMINGBIRD_PULLSPECUse oc -n lightwell-repo edit configmap imageset-configuration and change only that name: line. Do not copy example-imageset.yaml over the scored key.
The Job does not pass --remove-signatures. oc-mirror v2 still cannot land OCI referrers on this Nexus Docker dest, so the Job copies the image first, then copies tag-based signatures (.sig / .att / .sbom) with cosign copy. Do not add a flag that strips signatures.
oc -n lightwell-repo get configmap imageset-configuration \
-o jsonpath='{.data.imageset-config\.yaml}' | grep -E 'REPLACE_ME' \
&& echo 'STILL HAS PLACEHOLDERS' || echo 'placeholders gone'Run oc-mirror (learner Job)
oc-mirror is on Showroom PATH, but the scored run is the in-cluster Job so dest credentials and the workspace PVC are already wired.
oc -n lightwell-repo delete job oc-mirror-learner --ignore-not-found
oc -n lightwell-repo get configmap oc-mirror-tooling \
-o jsonpath='{.data.job\.yaml}' | oc create -f -oc -n lightwell-repo wait --for=condition=complete job/oc-mirror-learner --timeout=20moc -n lightwell-repo logs job/oc-mirror-learner -c oc-mirror
oc -n lightwell-repo logs job/oc-mirror-learner -c copy-signaturesRecord the dest digest from those logs (or dest registry metadata). Do not reuse only the 1.1 published digest as proof that dest is populated.
Check: internal cosign verify
Build a dest pull spec from:
-
dest_registry_host(userinfo) -
image path
hi/openjdk(not the Nexus Docker repo namedest_registry_repo/hummingbird-mirror) -
the dest digest you recorded from the Job
Or copy the DEST_PULLSPEC= line from the copy-signatures container log.
Then verify with the same Red Hat Hardened Images public key as 1.1. Dest TLS is lab-internal; allow an insecure registry if cosign requires it:
# Stub — fill DEST_PULLSPEC from Job logs + dest_registry_host. Not the worked UBI example.
export DEST_PULLSPEC='REPLACE_ME_DEST_PULLSPEC'
cosign verify \
  --allow-insecure-registry \
  --key https://security.access.redhat.com/data/63405576.txt \
  --insecure-ignore-tlog \
"${DEST_PULLSPEC}"The Job also grades ConfigMap report-02-hummingbird-mirror key learner_runs_mirror. Set it to learner-mirror. Empty or REPLACE_ME fails even if cluster state is correct. Do not copy validate-docs.
oc -n lw-poc-validate edit configmap report-02-hummingbird-mirrorThe scored Check is Job validate-02-hummingbird-mirror in lw-poc-validate. Direct nav URLs still work (honor system). Unlimited retries. There is no Solve.
oc -n lw-poc-validate delete job validate-02-hummingbird-mirror --ignore-not-found
TPL='job-02.yaml'
oc -n lw-poc-validate get configmap validate-job-templates \
  -o go-template="{{ index .data \"${TPL}\" }}" | oc create -f -
oc -n lw-poc-validate logs -f job/validate-02-hummingbird-mirror
Expect CHECK PASSED: before you continue. CHECK FAILED: names the object to fix. Delete the Job and create it again as often as you need.
Honor system: you can open Track 2 without a UI lock. The Check is still: ImageSet has no REPLACE_ME, Job oc-mirror-learner completed, and cosign verify used the internal digest.
Do not:
-
Point dest at a copied Showroom sample or UBI
-
Switch application
FROMhere (Track 3.2) -
Treat 1.1 public verify as sufficient for 1.2
Callout: Artifactory as dest
Your dest may be an Artifactory Docker remote or local cache rather than Nexus hosted Docker hummingbird-mirror. Author the ImageSet, run oc-mirror into that dest, and cosign verify the internal digest. This Check is the in-cluster Nexus dest.
Official documentation
-
Mirroring images with the oc-mirror plugin v2 (
ImageSetConfigurationmirror.openshift.io/v2alpha1,additionalImages) -
Verify the integrity of Red Hat Hardened Images (same public key as 1.1, now against dest)
Key takeaways
-
TSSC requires the signed base inside the trust boundary. You run the mirror. Dest does not arrive pre-loaded.
-
Internal verify is a different Check from published verify.
-
Signatures stay with the image because the Job copies them onto dest (Nexus stores the tag protocol, not OCI referrers).
-
Lightwell Network / Clearinghouse Premier do not replace this dest. Track 3
FROMuses it.
cd ~/ocp5-rhacs-showroom
bash setup/lab-cleanup.sh --module tssc-02