4.1 Source forbid-list
Overview
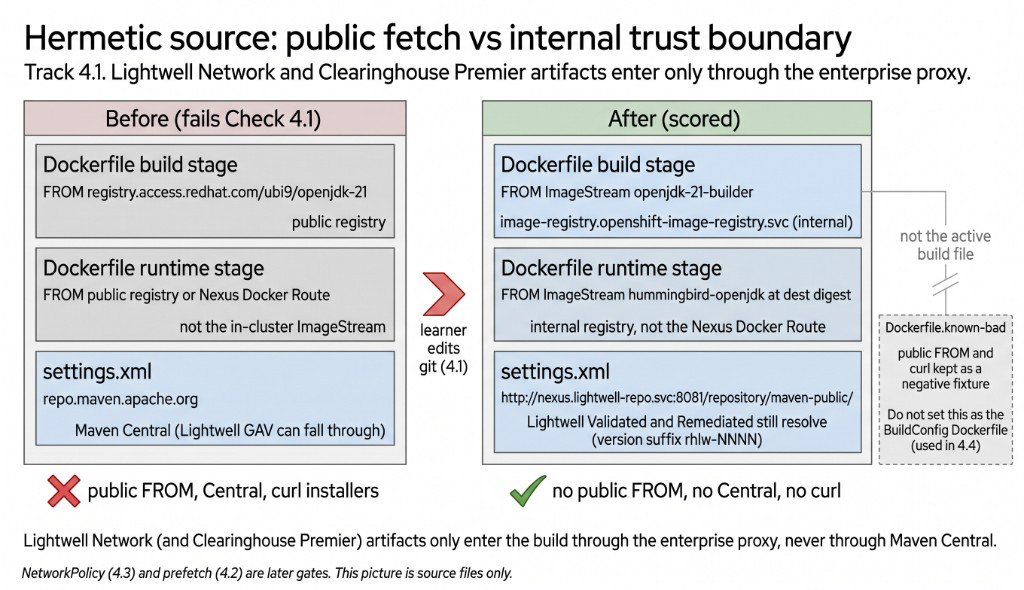
Hermetic starts in source. Strip public FROM, curl, and Maven Central from active files. Import a builder ImageStream. Retarget FROM. Keep Dockerfile.known-bad.
Why it matters
A Central remote bypasses the proxy the moment prefetch or NetworkPolicy is skipped. Lightwell Network GAVs and dest Hummingbird only enter the image if active Dockerfile and settings.xml have no public fallback. Keep Dockerfile.known-bad as the negative fixture 4.4 still uses.
Clearinghouse Premier does not add a public index. Member-specific GAVs must resolve from the same in-cluster Nexus service URL you point Maven at here.
What does it solve
-
Public
FROM, Maven Central, orcurlstill in active files -
Runtime
FROMstill on the Nexus Route that 4.3 will block
Seeded violations
Clone your app if needed (student_repo_url). Inspect:
cd /tmp/spring-boot-lw-poc
grep -nE 'FROM |curl |repo.maven.apache.org|registry.access.redhat.com|registry.redhat.io' Dockerfile settings.xml pom.xml || true
Expect at least: build-stage FROM UBI on registry.access.redhat.com, and repo.maven.apache.org in settings.xml.
Worked example (not the Check)
# Worked example ONLY — different public host. Do not use as the active Dockerfile.
FROM docker.io/library/eclipse-temurin:21-jdk
RUN curl -fsSL https://example.invalid/install.sh | sh
Your change: strip forbidden fetches; both FROM lines internal
-
While
build-egressis still too open, import a JDK builder intolw-poc-build(do not invent a Hummingbird builder digest — use the UBI JDK stream already on the seed, copied into the internal registry). Import dest Hummingbird the same way — 3.2’s runtimeFROMis the Nexus Docker Route, which 4.3 blocks:
BUILD_NS="$(oc -n gitea get configmap demo-userinfo-gitea -o jsonpath='{.data.student_build_namespace}')"
oc -n "${BUILD_NS}" import-image openjdk-21-builder \
  --from=registry.access.redhat.com/ubi9/openjdk-21:1.21 \
  --confirm
DEST="$(oc -n lightwell-repo logs job/oc-mirror-learner -c copy-signatures | grep '^DEST_PULLSPEC=' | cut -d= -f2-)"
echo "DEST=${DEST}"
oc -n "${BUILD_NS}" import-image hummingbird-openjdk \
  --from="${DEST}" --confirm --insecure=true
oc -n "${BUILD_NS}" get istag hummingbird-openjdk:latest \
-o jsonpath='{.image.dockerImageReference}{"\n"}'-
Point the Dockerfile build
FROMat ImageStreamopenjdk-21-builder(internal registry). Point runtimeFROMat ImageStreamhummingbird-openjdkusing the dest digest from 1.2 / 3.2 (image-registry.openshift-image-registry.svc:5000/${BUILD_NS}/hummingbird-openjdk@sha256:…). Do not leavedest_registry_host(the Nexus Docker Route) on an activeFROMline. Noregistry.access.redhat.comon activeFROMlines. -
In
settings.xml, removerepo.maven.apache.orgfrom the Lightwell profiles. Point remotes at the in-cluster Nexus service (nexus_internal_urlfrom userinfo —http://nexus.lightwell-repo.svc:8081), not the HTTPS Route. Add a<mirror>withmirrorOf(orexternal:) whose URL is${nexus_internal_url}/repository/maven-public/. Seededmaven-publicincludes Validated + Remediated so.rhlw-*pins resolve. 4.3 will block the Nexus Route fromlw-poc-build; the service URL keeps working. -
If
Dockerfile.known-badis missing from your clone, copy it from the seed (publicFROM/curl). The template repo already includes it. Do not set it as the BuildConfig Dockerfile. 4.4 still uses that file as a negative.
cd /tmp/spring-boot-lw-poc
git add Dockerfile settings.xml Dockerfile.known-bad
git commit -m "Forbid-list: internal FROM and Nexus-only Maven remotes"
git push origin HEAD
Check: scan of active files
cd /tmp/spring-boot-lw-poc
git show HEAD:Dockerfile | grep -E '^FROM '
git show HEAD:settings.xml | grep -E 'repo.maven.apache.org|lightwell-repo' || true
test -f Dockerfile.known-bad && echo 'known-bad fixture present'
Pass when active Dockerfile / settings.xml have no public FROM, no dest-registry Route, no Central, no curl installers — and Dockerfile.known-bad still exists. Both FROM lines use the internal registry.
The Job also grades ConfigMap report-08-forbid-list key hermetic_starts. Set it to source. Empty or REPLACE_ME fails even if cluster state is correct. Do not copy validate-docs.
oc -n lw-poc-validate edit configmap report-08-forbid-listThe scored Check is Job validate-08-forbid-list in lw-poc-validate. Direct nav URLs still work (honor system). Unlimited retries. There is no Solve.
oc -n lw-poc-validate delete job validate-08-forbid-list --ignore-not-found
TPL='job-08.yaml'
oc -n lw-poc-validate get configmap validate-job-templates \
  -o go-template="{{ index .data \"${TPL}\" }}" | oc create -f -
oc -n lw-poc-validate logs -f job/validate-08-forbid-list
Expect CHECK PASSED: before you continue. CHECK FAILED: names the object to fix. Delete the Job and create it again as often as you need.
Honor system: 4.2 still opens.
Callout: pip forbid-list
On a pip app the same grep is pypi.org / public index-url in requirements.txt and pip.conf, not Maven Central. This Check is Dockerfile + settings.xml.
Official documentation
-
Lightwell Network Java repository (the remotes that must remain after Central is gone)
-
Konflux mapping (hermetic source policies → this Check)
Key takeaways
-
TSSC hermetic starts in source, before NP and prefetch.
-
Lightwell Network and Clearinghouse Premier GAVs stay on the internal Nexus service. Konflux hermetic source policies map to this Check. Product names are in Konflux mapping.
cd ~/ocp5-rhacs-showroom
bash setup/lab-cleanup.sh --module tssc-08